Security & Permission Boundaries
Autonomy without control is dangerous. ATHREUS is engineered with explicit permission barriers, local cryptographic token authentication, and honest boundaries.
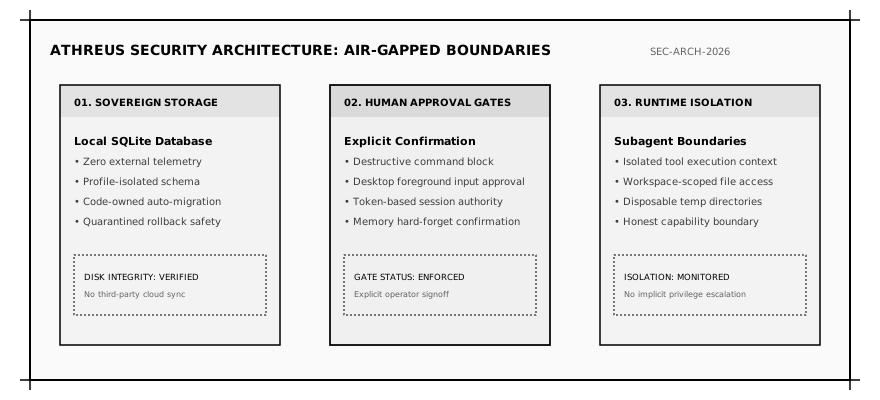
Local-First Storage
Your data, memory cards, and transcripts remain on your local disk in SQLite files. No centralized telemetry, tracking beacons, or unsolicited sync.
Human Confirmation
Destructive terminal commands, desktop foreground controls, and file overwrites pause for operator sign-off. Agents cannot bypass confirmed gates.
Token-Based API Security
All Studio API and MCP requests are signed with temporary profile tokens. Local login lockfiles protect single-user environments from unauthorized web requests.
Operating System Isolation Boundaries
ATHREUS enforces strict workspace directory conventions, execution budgets, and permission gates. However, workspace file scoping and tool barriers do not constitute a hardware-level hypervisor VM sandbox unless deployed inside a dedicated Docker container. For running untrusted arbitrary code, always deploy ATHREUS inside isolated container instances.